On this page
For about twelve years, most of what I did in public, I did on one Twitter account: @sniko_. It's gone now. Someone else has the handle, and I post from @0x11b6.
I never kept a backup, so this is pieced together from the Wayback Machine and old news articles. The links are there if you want to check.
I joined in January 2011
I joined Twitter in January 2011. By 2018 my bio was basically a list of side projects:
Views are my own. // @mycrypto // Maintains etherscamdb.info, eth-phishing-detect, @EthAddrLookup, ESL, @CryptoPhishing
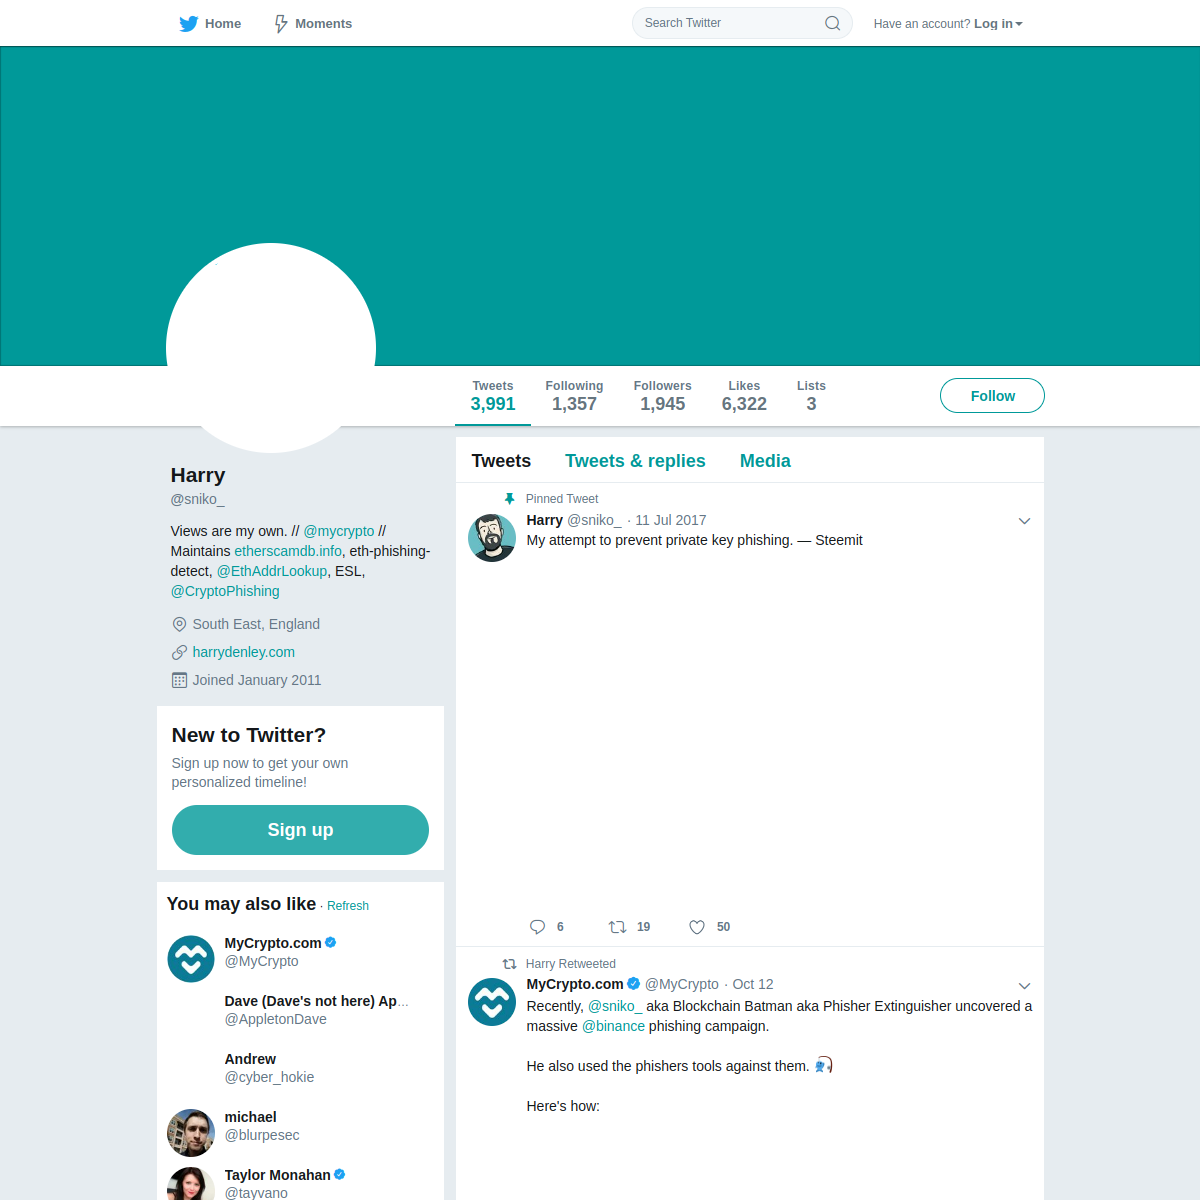
14 October 2018. My display name was just "Harry". (archive)
I changed the bio whenever the work changed. In 2019 it was "security & antiphishing @ @mycrypto", plus "Lead Fishing master in residence at @meta_cartel Ventures", which I stand by. By 2022 it was "Security at @MetaMask". My follower count crept up for years, and then it didn't creep:
| Date | Followers | Following |
|---|---|---|
| 14 Oct 2018 | 1,945 | 1,357 |
| 27 Sep 2019 | 2,538 | 1,956 |
| 21 Nov 2020 | 3,802 | 2,448 |
| 14 Apr 2021 | 5,899 | 2,563 |
| 13 Nov 2021 | 9,053 | 2,684 |
| 8 Aug 2022 | 15K | 3,023 |
| 15 Jul 2023 | 17.6K | 3,196 |
Most of that came from 2021 on, when DeFi and NFTs brought a lot of new people in, and a lot of scammers came after them.
What I got done with it
The account was never the point. It was where I put the work so people would see it before they got phished. Looking back, these are the things I'm glad I did with it:
- EtherAddressLookup (2017). A browser extension that warned you before you landed on a known crypto phishing domain. Back then hardly anything did that. At one point it had around 120,000 users. In 2018 WIRED wrote about it and about EtherSecurityLookup, its sibling that flagged Twitter accounts impersonating well-known people in crypto.
- Calling out Centra before its ICO (2017). I wrote up my doubts about Centra's ICO, including whether its listed CEO was a real person. When two of the founders resigned a few months later, Business Insider cited the post.
- The WalletGenerator.net backdoor (2019). At MyCrypto we found that WalletGenerator.net was serving code that could reproduce the "random" keys it gave people. Ars Technica and Decrypt both covered it.
- Counting Twitter giveaway scams (2019). I tracked the fake "send 1 ETH, get 10 back" accounts and found they had grown 95% in a year. Decrypt wrote up the report.
- Getting 49 fake wallet extensions pulled from Chrome (2020). They were all phishing for seed phrases. I shared the list with ZDNet, and Google removed them.
- Getting stolen funds back (2020). In one fake-Uniswap phishing case the scammer's database was wide open. I traced the funds to Binance and worked with them to get the money back to the victim. Decrypt and CryptoPotato both covered it.
- WHG_1 (2020). I swept unclaimed UNI out of compromised addresses before the attacker could, so it could go back to the owners. The tweets about it are below.
- The blue check, in 2021. I'll come to that next.
My blue check, back when you couldn't buy it
In 2021 I applied through Twitter's verification process and was approved. This was the old blue check, the one Twitter gave to accounts it judged notable and authentic. You couldn't pay for it. I got it between April and September 2021 (before, after), while I was at MyCrypto doing phishing and security research and tweeting most of it as it happened.
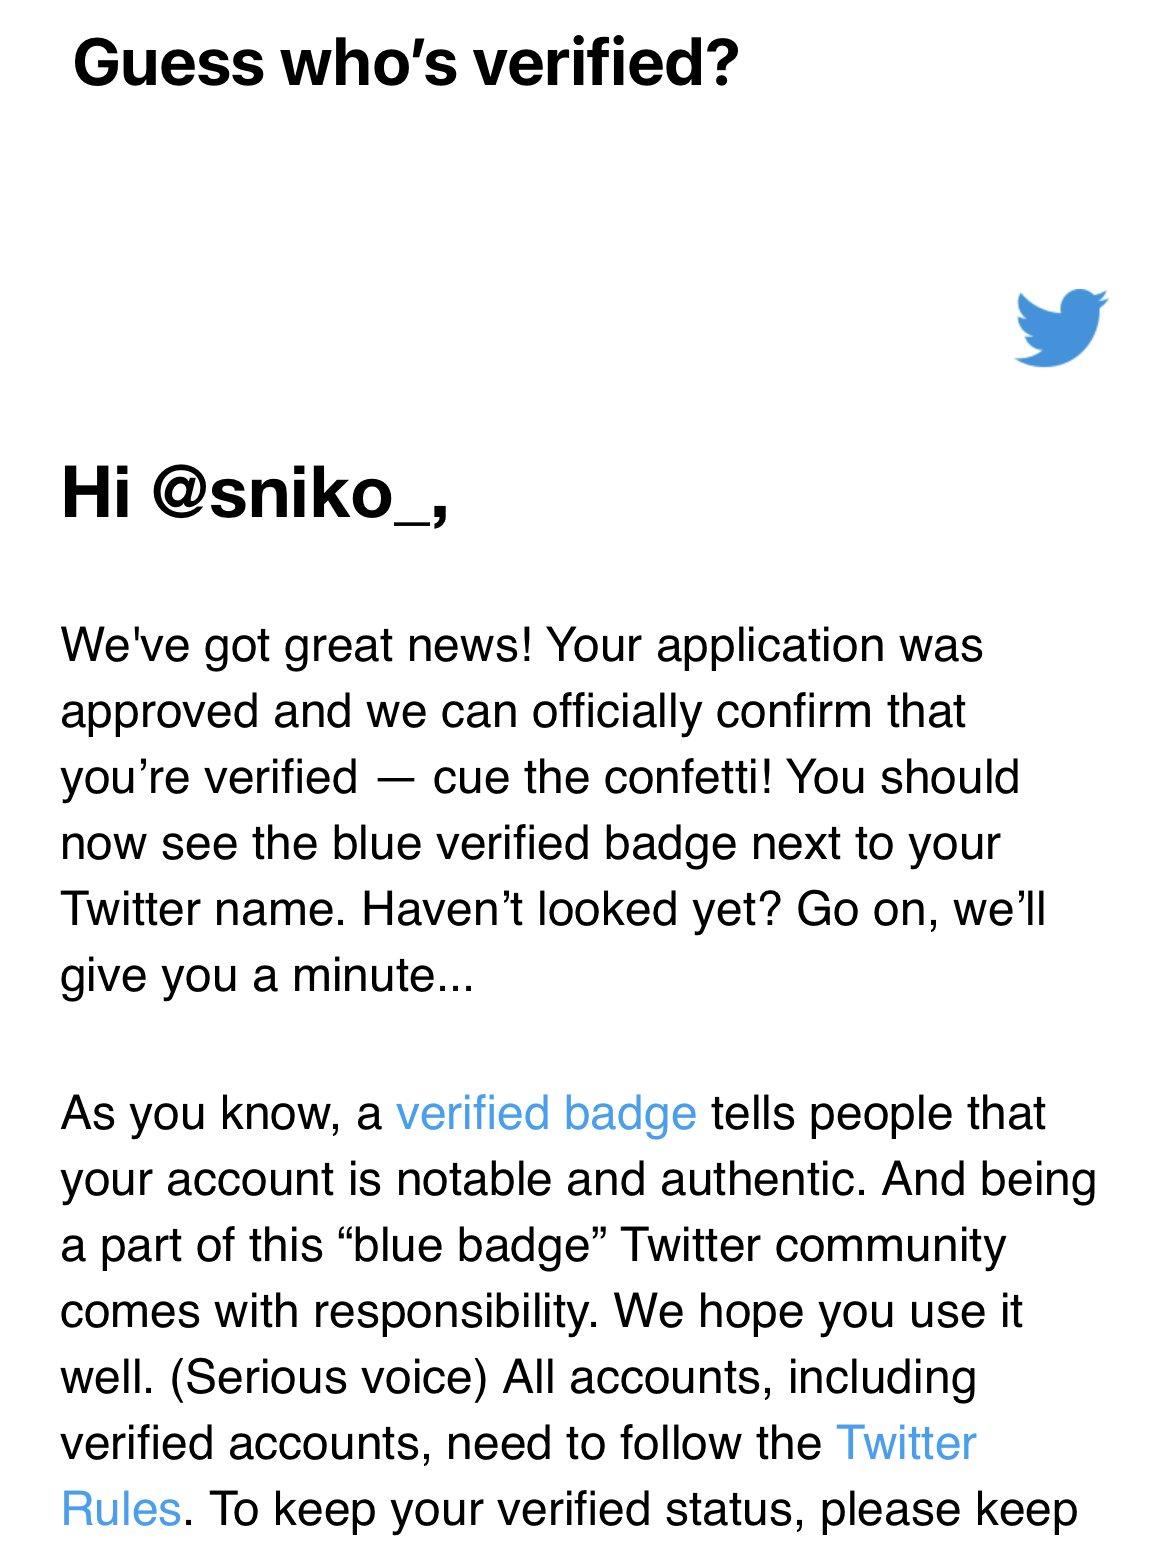
The email from Twitter telling me my application had been approved.
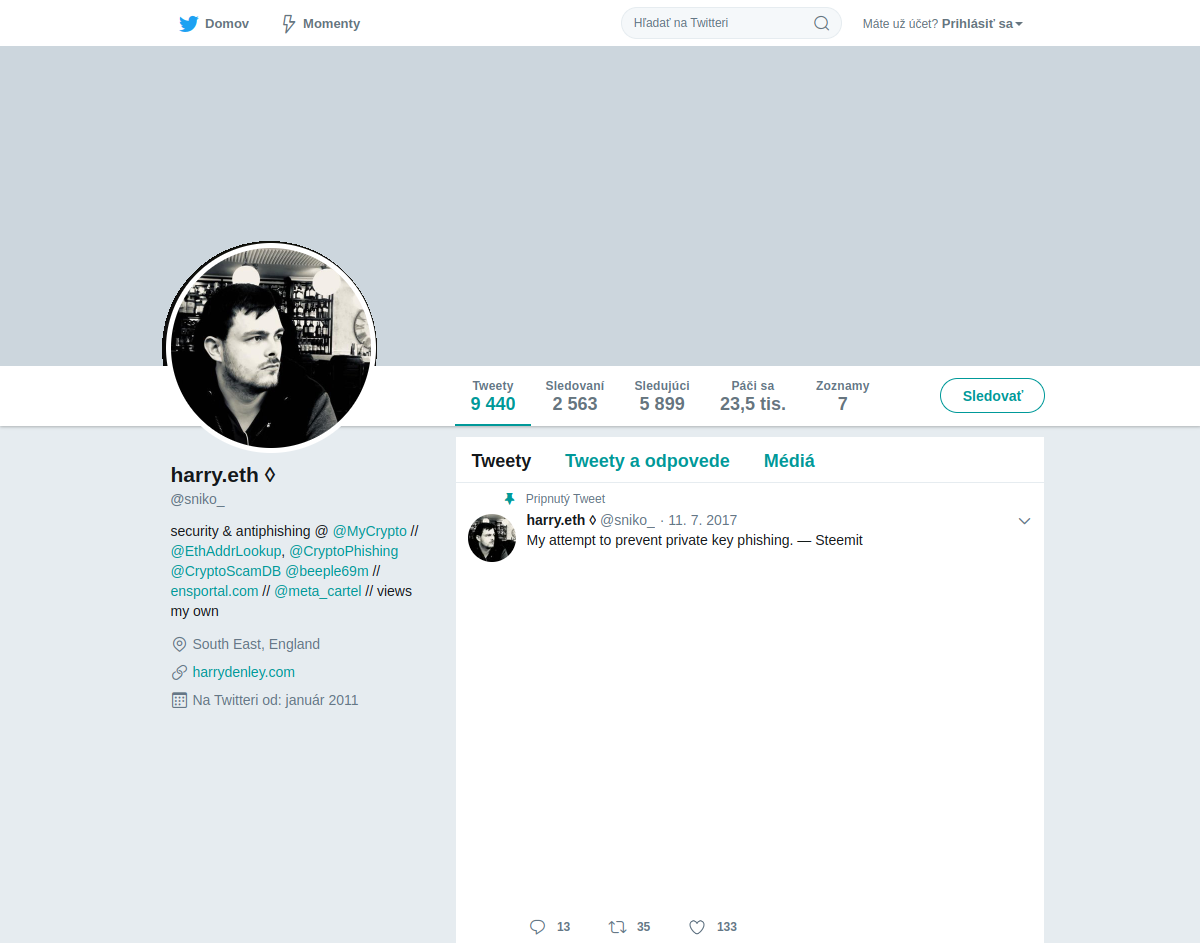
14 April 2021, no badge yet. (archive)
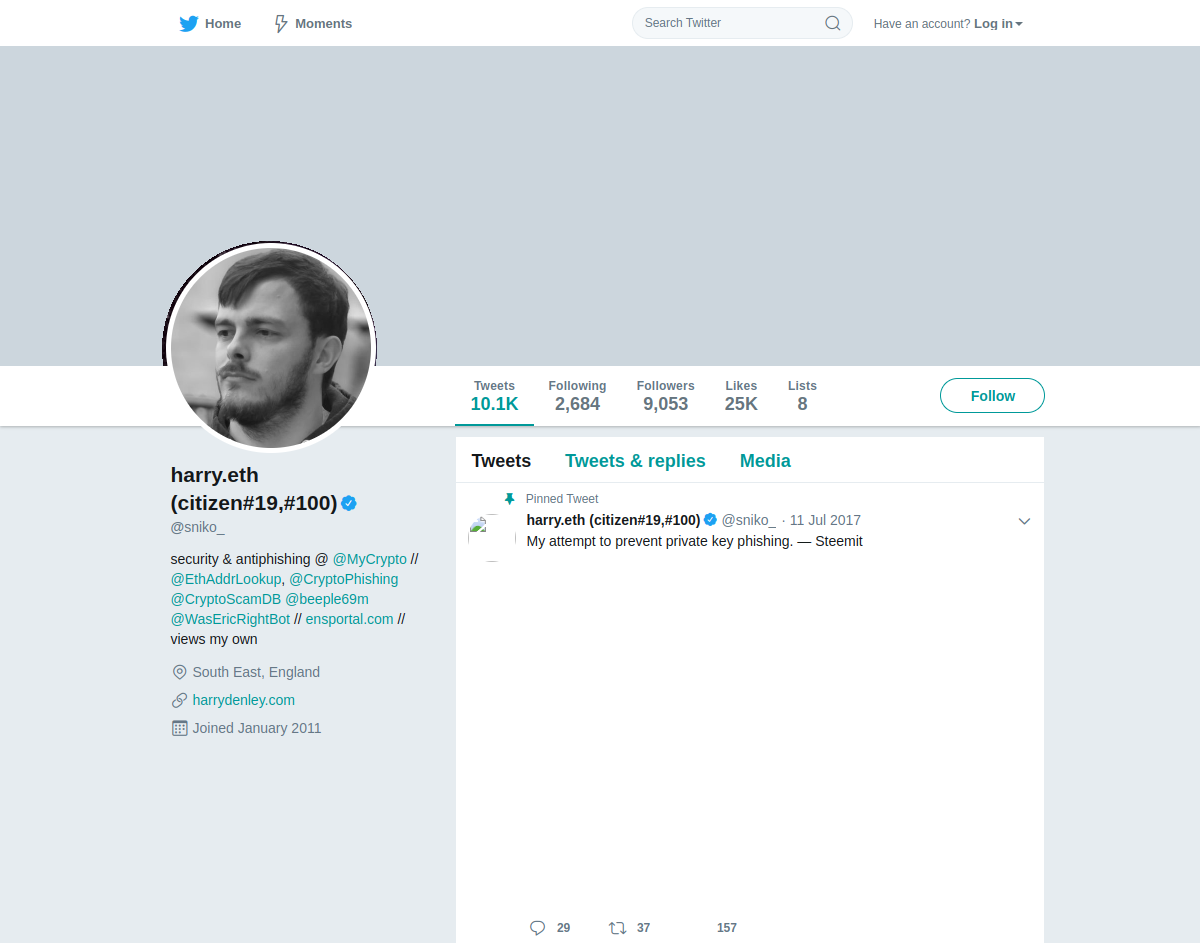
13 November 2021, verified. (archive)
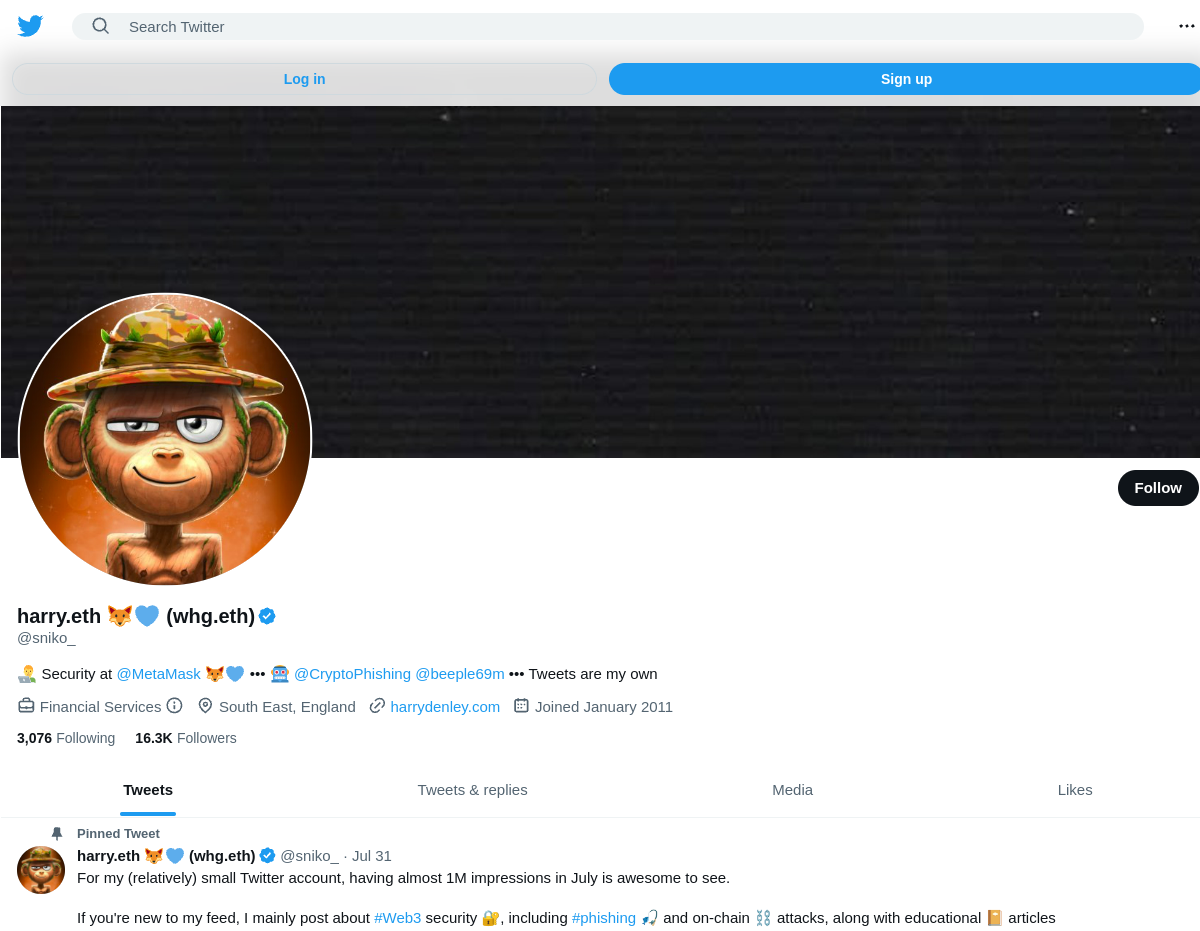
24 November 2022. Still the legacy check, and by now I was at MetaMask. (archive)
In November 2022, after Elon Musk bought the company, Twitter started charging $8 a month for a blue check. On 20 April 2023 it began removing the legacy checks from everyone who didn't pay (Reuters covered it too). I didn't pay, so I lost mine.
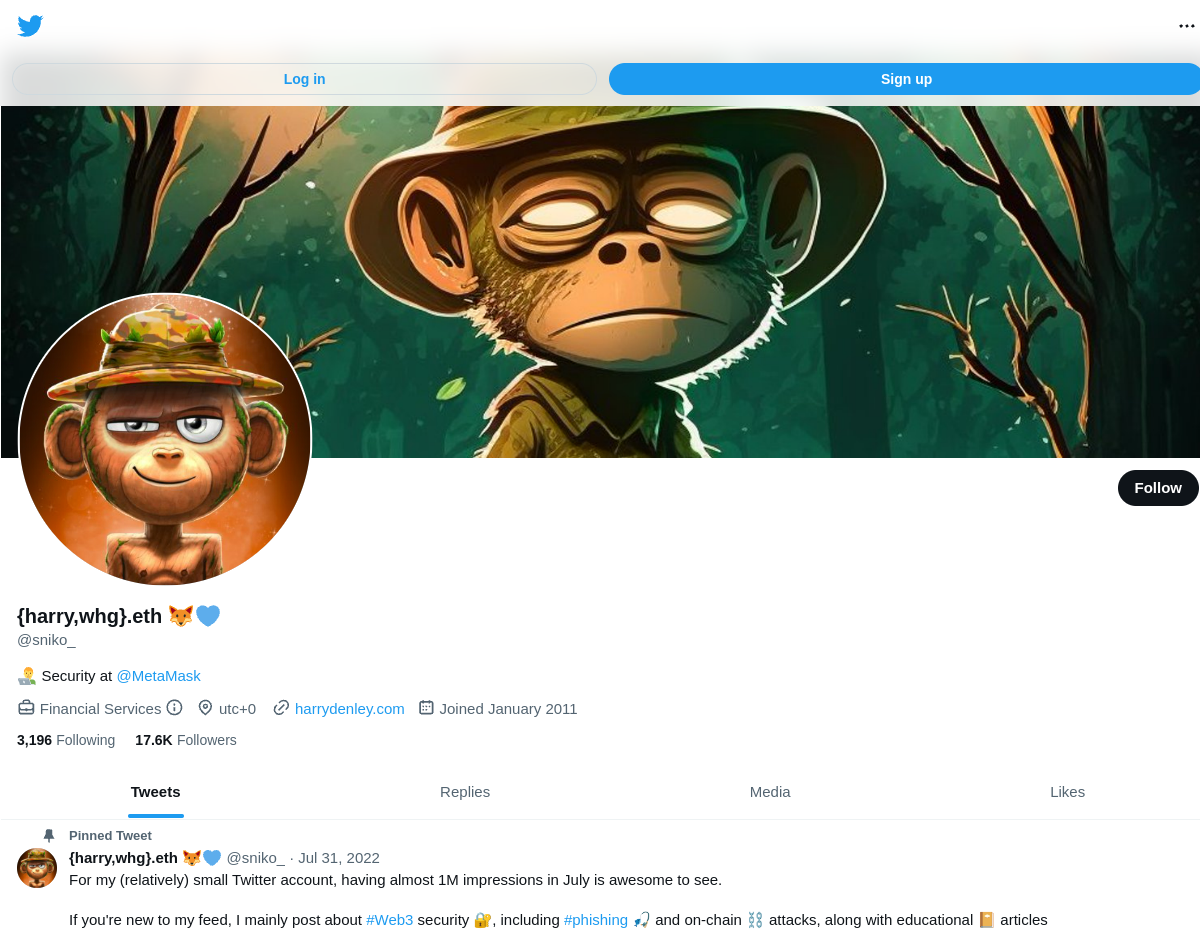
15 July 2023, after the legacy checks went. (archive)
When the press picked up my tweets
A lot of my threads ended up in news articles, usually because I was one of the first to spot something and say it out loud. These are the ones I could find that embed or quote a tweet from @sniko_ directly. Since the account is gone, most of those embeds are now broken.
- Cointelegraph, December 2019. My warning that the "Shitcoin Wallet" Chrome extension was injecting JavaScript to steal passwords and keys. (article)
- ZDNet, March 2020. My tweet about a fake Ledger Chrome extension that was being promoted with Google ads. (article)
- Cointelegraph, March 2020. The fake Bitcoin QR code generators I found on 22 March, which had stolen over $40,000 in a month. (article)
- Decrypt, July 2020. My phishing thread from 9 July, embedded in the story about getting a victim's funds back. (article)
- CryptoCoin.News, March 2021. My investigation of the malware being pushed by SushiSwap impersonators. (article)
- The TreasureDAO exploit, March 2022. I tweeted that the marketplace's
buyItem()didn't check for a quantity of zero, so people could take NFTs for 0 MAGIC. Cointelegraph, ZDNet and rekt.news all used those tweets. - Beeple's hacked account, May 2022. I flagged that the "raffle" link on Beeple's account was a wallet drainer. Decrypt and Metro embedded the tweet.
- The Uniswap LP phishing attack, July 2022. Cointelegraph said I was "one of the first to raise the alarm bells", after I tweeted that 73,399 addresses had been sent a malicious token. (article)
- Azuki's account takeover, January 2023. My tweet saying MetaMask was blocking the phishing domain. (Decrypt)
- The CZ death rumour, March 2023. I called it the "2023 adaptation of attempted market manipulation" and suggested a proof of life using the latest BNB Smart Chain block hash. (Cointelegraph)
Plenty of other pieces quoted me or my write-ups without embedding a tweet. They're all on my press page.
Some tweets worth keeping
A lot is missing, but these are the ones I'd have kept anyway.
11 July 2017. From the early days of the anti-phishing work.
My attempt to prevent private key phishing. — Steemit
(archive)
12 October 2018. This one wasn't mine. MyCrypto posted it after I wrote up a Binance phishing campaign and turned the phishers' own tools against them. I'm keeping it for the nickname.
Recently, @sniko_ aka Blockchain Batman aka Phisher Extinguisher uncovered a massive @binance phishing campaign. He also used the phishers tools against them.
(archive)
25 September 2019. Still true.
Are you learning command line? Do you copy/paste commands into your console as you read documents? Well, you shouldn't. With this simple #css "trick", you can copy #malicious commands without you realising.
(archive)
17 September 2020. This was during WHG_1, when I was rescuing tokens from compromised addresses before the attacker could, so they could go back to their owners.
i am tired and i just spent a combined 0.066509845ETH/$25 to inefficiently sweep unclaimed 400 $UNI from a compromised address [...] gas prices pls go down it is becoming expensive to sweep with the intention of reuniting the $UNI with their owners
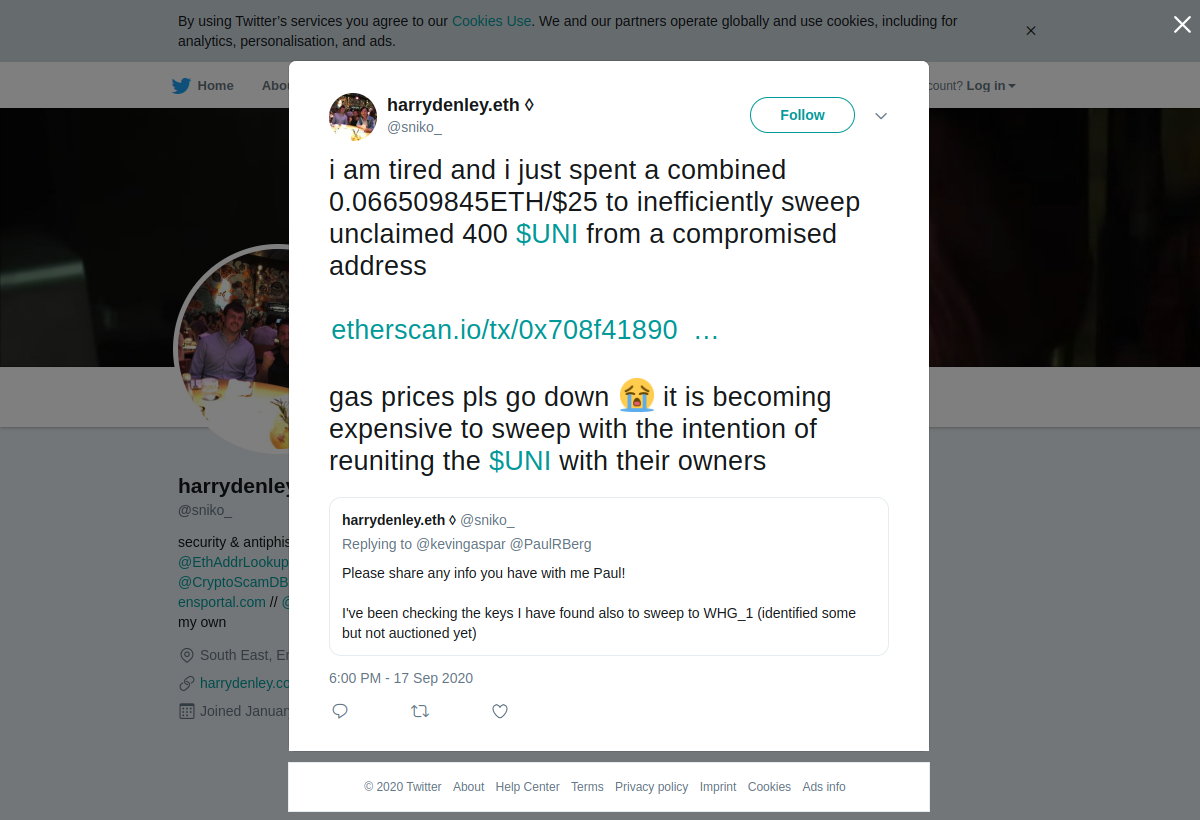
17 September 2020. (archive)
23 March 2021. Six months later:
It has been 185 days. The $UNI I rescued from the compromised accounts, as part of the WHG_1 effort, went from ~$7,237 to ~$39,734 (combined) Zero requests from the owners so far
(archive)
16 September 2021. A scam token airdrop that was going around that month.
It looks like it is "free-airdrop-worth-a-lot-but-is-a-scam" season. Can't sell on Uniswap. Approve() will always revert directing you to a website. Website will ask you to claim reward, then sweep your highest holding ERC20
(archive)
4 November 2021. This got 1,493 likes and 457 retweets, more than anything else I found in the archive. My point was that the preview card Twitter shows you isn't proof of where a link goes.
Does this link take you to Uniswap? Do you trust it because Twitter says it takes you to Uniswap? Why don't you click to find out?
(archive)
12 November 2021. A phishing bot was posting in the ENS server and sending what it collected to a webhook. I flooded the webhook so it would start returning 429s before any secrets got through.
There is a malicious bot targeting @ensdomains server, posting a phishing @Collab_Land_ domain to steal your @MetaMask secrets I am flooding the webhook to 429 the bot to prevent secrets being sent
(archive)
Kind words from the timeline
I'd have liked to list who followed me, but no record of that survived, and I'm not going to list names from memory. A few nice things people said about me did:
- MyCrypto, October 2018: "@sniko_ aka Blockchain Batman aka Phisher Extinguisher". (archive)
- MyCrypto, October 2021: "@sniko_ has been a part of MyCrypto forever, and has built up a reputation as both an amazing person and a world-class security expert." (archive)
- MyCrypto, October 2021: "The safety of your cryptocurrency is constantly on our mind. Part of that reason is because @sniko_ is on our team and he's helped foster a security-first environment." (archive)
- Week in Ethereum News, September 2021, put my airdrop scam thread under #MostClicked: "@sniko_ airdrop revert directs to scam site". (archive)
So where did it go?
My own fault. I deactivated the account and forgot to log back in within 30 days, so Twitter deleted it for good. By the time I noticed, someone else had already registered the handle, and @Sniko_ is now an unrelated account that joined in July 2024.
So years of my phishing write-ups, incident threads and late-night sweeps are gone, apart from what the Wayback Machine kept. If you ever linked to one of my @sniko_ tweets, that link is dead.
I'm @0x11b6 now
You can find me on X at @0x11b6. It's the same work under a new handle. Come say hi.